
Security
How we look after the security of what we build
We build and run our own systems: Vendor ERP, Agenvia and Gridio. This page explains who is in charge of security, what we do, what it covers, and how to tell us if you find a problem.
Ownership
Who is in charge of security
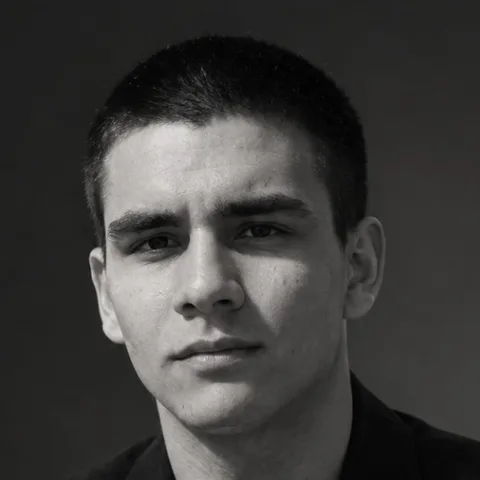
Brandon is Nexvia’s co-founder and CTO. Since 2023 he has designed, built and operated the platform, focused on making the software hold up in production for real businesses. He is also the person accountable for security: he reviews the code and infrastructure of our products and handles the reports that come in.
Track record
-
2023 - present
Co-founder and CTO, Nexvia Solutions
Leads the architecture, development and operation of the platform: Vendor ERP (multi-tenant SaaS in production), the WhatsApp Cloud API integration and end-to-end monitoring.
-
2026
Internal security audit
Led an internal security audit of the platform, assisted by AI tools. Fixed the critical infrastructure findings and built an isolated test environment to verify each fix.
-
2022 - 2025
IT administrator, Agrocentro Hasenkamp
Automation of databases, price lists and inventory control.
Education and credentials
- Software Engineer, HackerRank (July 2025)
- Google IT Support, Google (June 2025)
- Google IT Automation with Python (course)
- ML Developer Career, Anyone AI
- University Technical Degree in Information Technology, Universidad Kennedy (in progress)
What we do
Security work on our own systems
Code and infrastructure review
We review the code of our products, our servers, the connections between them and the configuration of our whole infrastructure.
Internal audit in 2026
We ran an internal security audit. The infrastructure findings are fixed and we are still working through the code-level ones.
Monitoring
We centralize the logs and metrics of our services so we can spot abnormal behavior in time.
Testing in our own environments
Security testing is done only against systems we own, including isolated lab environments we control.
How we work
- Changes go through a branch, a review and a test environment before reaching production.
- Infrastructure changes are made outside the hours when customers operate, unless they respond to an incident already under way.
- Secrets and credentials are not kept in code, and when they are rotated every place they are used gets checked.
- Each security fix is verified with a test that repeats the attack, in an isolated environment with no real data.
- Our own mistakes are written down so we do not repeat them.
Scope
What this page covers
We accept reports about the systems we operate. So that a report can be handled quickly, it helps to know what is in and what is out.
In scope
- nexviasolutions.net Corporate website and its subdomains
- vendor.nexviasolutions.net Vendor ERP, management and point of sale
- agenvia.app Agenvia
- gridio.net Gridio
Out of scope
- Data, accounts or information belonging to other people or companies.
- Denial-of-service attacks and mass automated testing that generates load.
- Social engineering or phishing against our team or our customers.
- Physical access to offices or equipment.
- Failures in third-party services (for example Meta, Mercado Pago or Google): report those to them.
Reports
How to report a vulnerability
Email our security mailbox. The clearer the report, the faster we can reproduce and fix it.
What to include
- Which system or address is affected.
- What you found and the impact you think it has.
- The steps to reproduce it, or a proof of concept.
- How we can reach you if we need more details.
We ask that you
- Do not access, change or delete other people’s data.
- Do not disrupt the service.
- Do not disclose the issue until we have had a chance to fix it.
Security contact
security@nexviasolutions.net
If the button does not open your mail app, copy the address or open it in Gmail.
We also publish this information at /.well-known/security.txt.
What happens next
Four steps from the moment you write to us
We acknowledge
We aim to confirm we received it within 5 business days.
We assess
We reproduce the problem, measure how serious it is and, if needed, ask you for more information.
We fix
We prioritize by the real risk to the people and companies using the system.
We let you know
Once it is fixed we tell you, and we agree with you on when it can be talked about publicly.
About rewards
We do not currently run a monetary rewards program. We do value responsible disclosure a great deal and, if you like, we credit your contribution when the fix is published.
Last updated: October 2026.